Veylqorix — Code-security gate platform
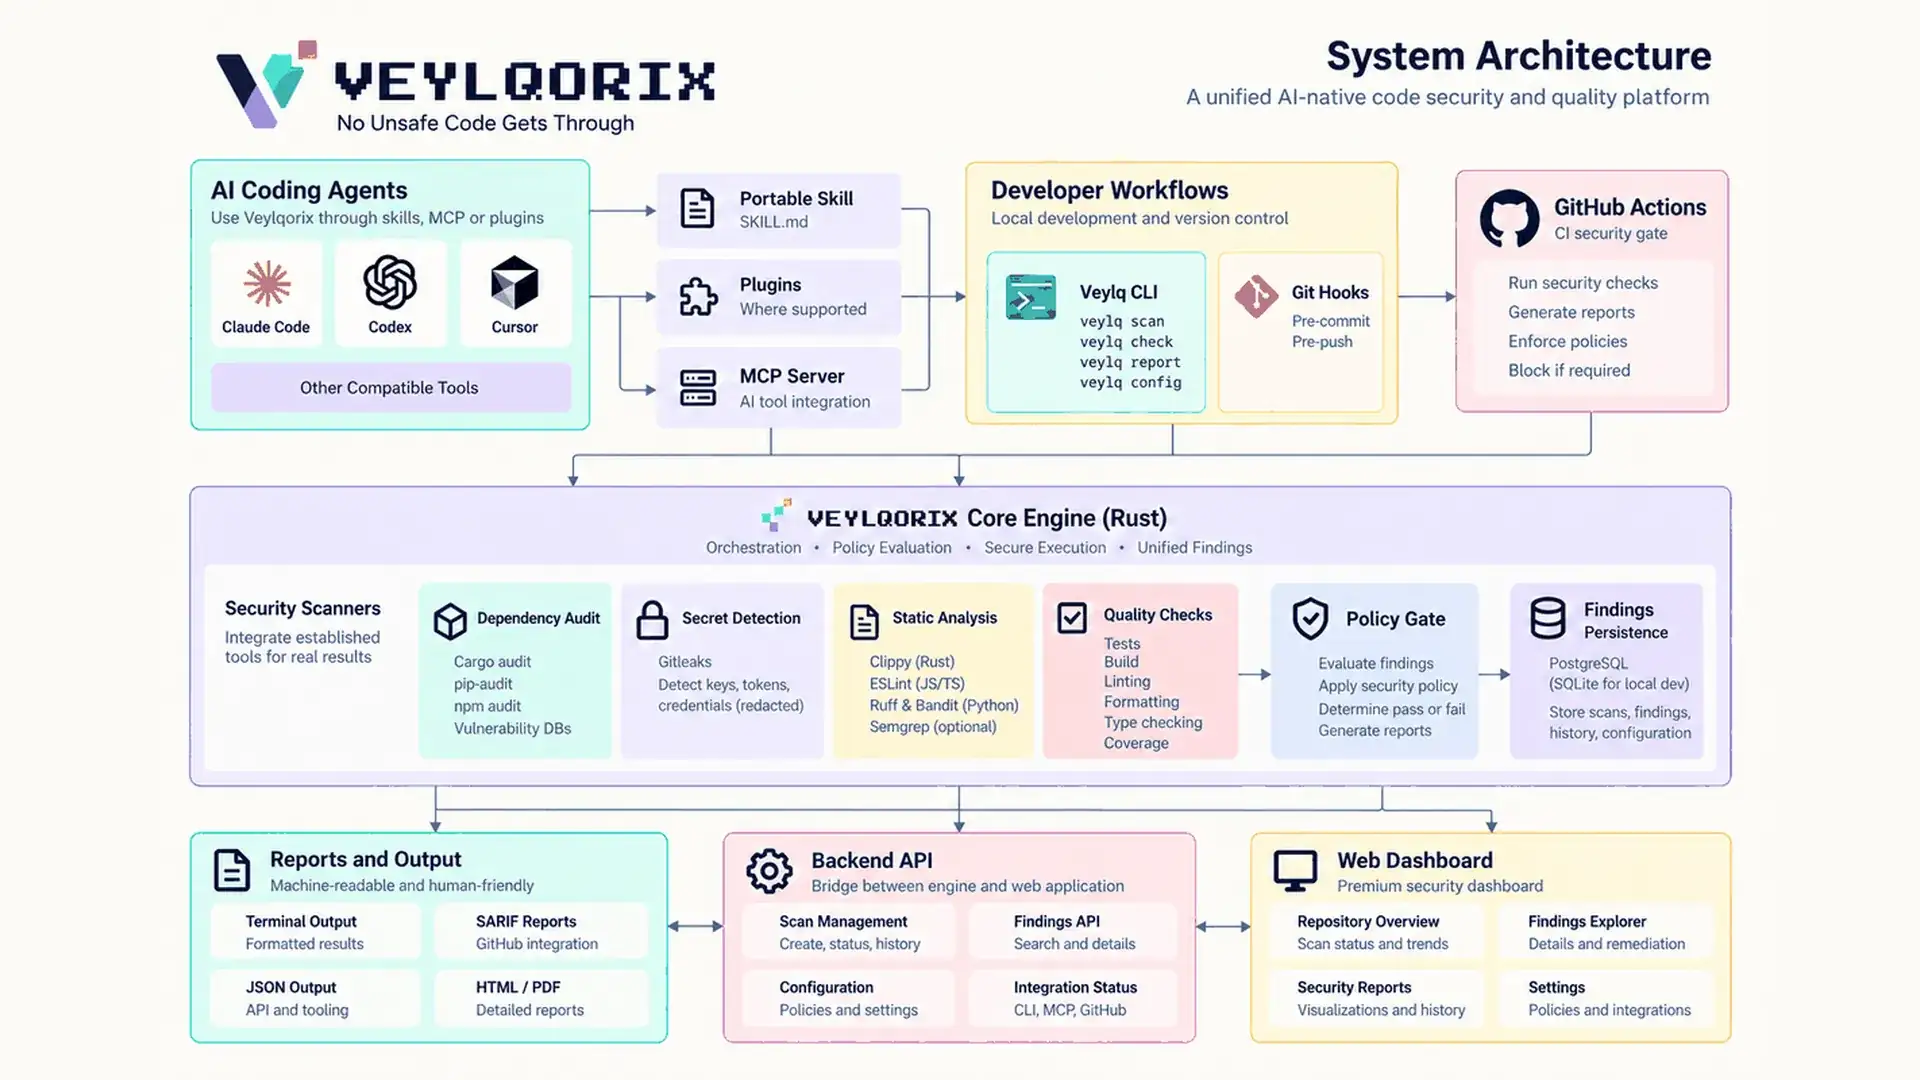
newVeylqorix is a code-security and quality gate platform built as a TypeScript/pnpm monorepo plus a standalone Rust security engine. It orchestrates real scanners — dependency auditing, secret detection, license checks, static analysis, and test suites — normalizes their output into one finding schema, and emits a deterministic gate decision (PASS / FAIL / INCOMPLETE, stable exit codes 0/1/2) with auditable evidence. CLI, MCP server, API, GitHub Actions, and agent skills are all thin adapters over that single engine, and an agent-safe policy means an AI agent can't suppress a finding. MIT-licensed, with sample data clearly labeled as sample.
Live demo
The running product, embedded below. If it refuses to load in an embed, the live site opens in a new tab.
Problem
Security gates are either single scanners or brittle scripts: findings land in a dozen different formats, skipped or errored checks quietly count as clean, and teams can't prove what a gate actually checked.
Solution
Veylqorix is a TypeScript/pnpm monorepo plus a standalone Rust security engine. The engine runs real scanners — dependency auditing, secret detection, license checks, static analysis, test suites — normalizes every result into one finding schema, and produces a deterministic gate decision with stable exit codes (0 PASS, 1 FAIL, 2 INCOMPLETE). CLI, MCP server (6 tools), API, GitHub Actions and skills are all thin adapters over that single engine, and an agent-safe policy means an AI agent can't suppress a finding.
Decisions I made
- 01INCOMPLETE as its own exit code (2) — a skipped or errored mandatory check degrades coverage and can never read as a clean pass; most pipelines collapse 'we didn't look' into green.
- 02Rust engine, TS adapters — the verdict has to be identical whether it's made in CI, by the CLI, or by an agent calling the MCP tools; one engine, six thin adapters.
- 03Agent-safe policy — suppression and policy edits come from a human-owned channel only; an agent can request a review, never remove a finding, and the audit trail records every change.
- 04Sample data labeled as sample — presenting a synthetic scan as live results would erode the exact trust the product is trying to build.
Outcome
No unsafe code gets through, and no silent gaps either — a skipped mandatory check or scanner error degrades coverage and is marked SKIPPED/ERROR, never mistaken for a clean pass. Sample data is explicitly labeled, never presented as live results.
This project is part of the work I ship as a developer-tools engineer — see the freelance services page for project types, process, and how to start.